Hello Hackers! 👋
I hope you’re all doing great, continuing to secure the digital landscape, and contributing to the ethical hacking community! 🛡️💻
Today, I’m excited to share how I hacked the Dutch Government (Government Of Netherland 🇳🇱) and got appreciated by them officially! 🎉📜
🕰️ Backstory
About 2 years ago, I found a vulnerability in a Dutch government domain. At that time, I was a beginner and didn’t realize the domain belonged to the government. I randomly selected a target, found a flaw, and reported it via the website's email.
✅ Result:
After one year, I received a reply with a $25 bounty and appreciation for my report! 🥳
Full Article Link: Here
🎯 Targeting the Dutch Government Again
This time, I decided to intentionally target the Dutch Government for a bigger achievement and recognition. 🏆
📌 Note: I can’t disclose the exact domain or vulnerability due to ongoing patching
and security policies. So let’s just call the target: abc.nl
🔍 Reconnaissance Phase
I started by exploring the public scope of Dutch Government domains:
Dutch Government Subdomain Scope
I picked one domain and began manual subdomain discovery using browser tools like Wappalyzer.
🛠️ Tip:
Automatic recon is good, but manual recon is the real game-changer! 💪🔥
📁 Vulnerability Discovery
While checking the subdomains manually, I found one using an Nginx server with a reverse proxy. I performed directory brute-forcing using:
🔎 During fuzzing, I discovered a .file one which responded with HTTP 200 OK.
📄 This file is automatically generated by IDE and contains metadata about the backend project structure.
❗ This was sensitive information not meant to be publicly accessible and it wasn’t restricted.
📸 Reporting and Acknowledgment
I gathered all the screenshots and prepared a solid Proof of Concept (PoC). I reported it immediately. ⏱️
📩 Next Day:
I received confirmation that the vulnerability was valid! ✅
📅 After a few days:
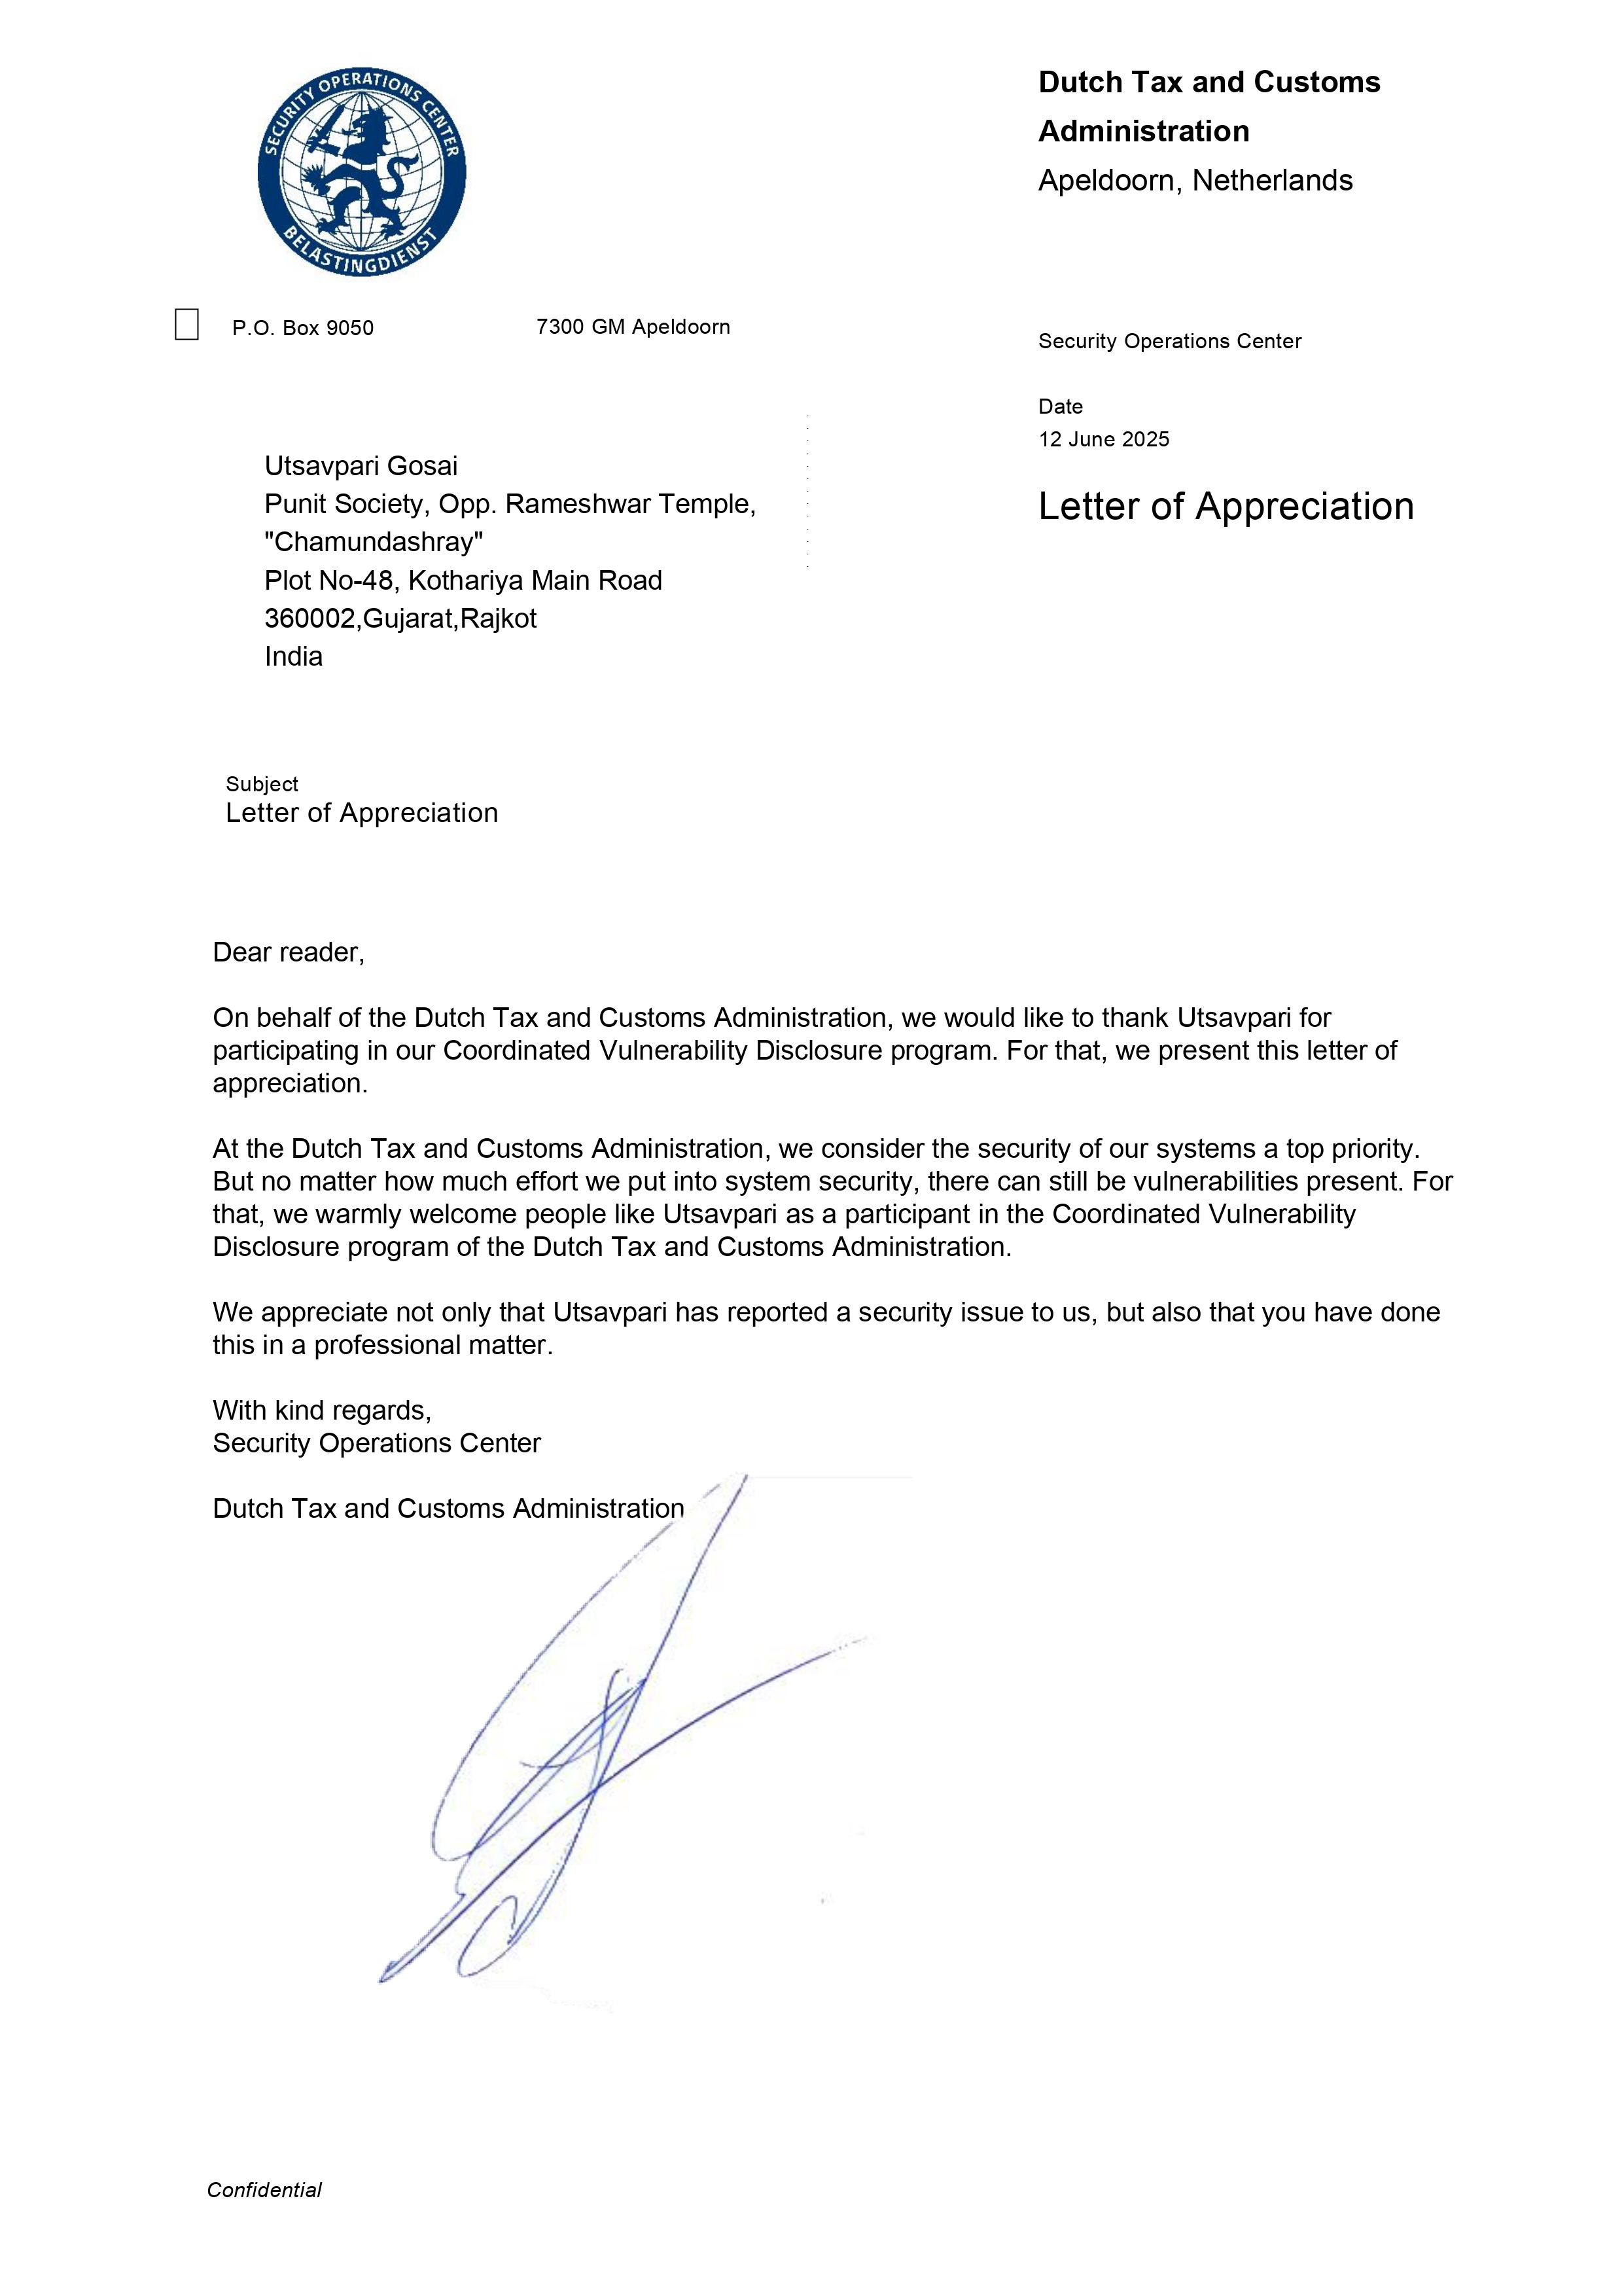
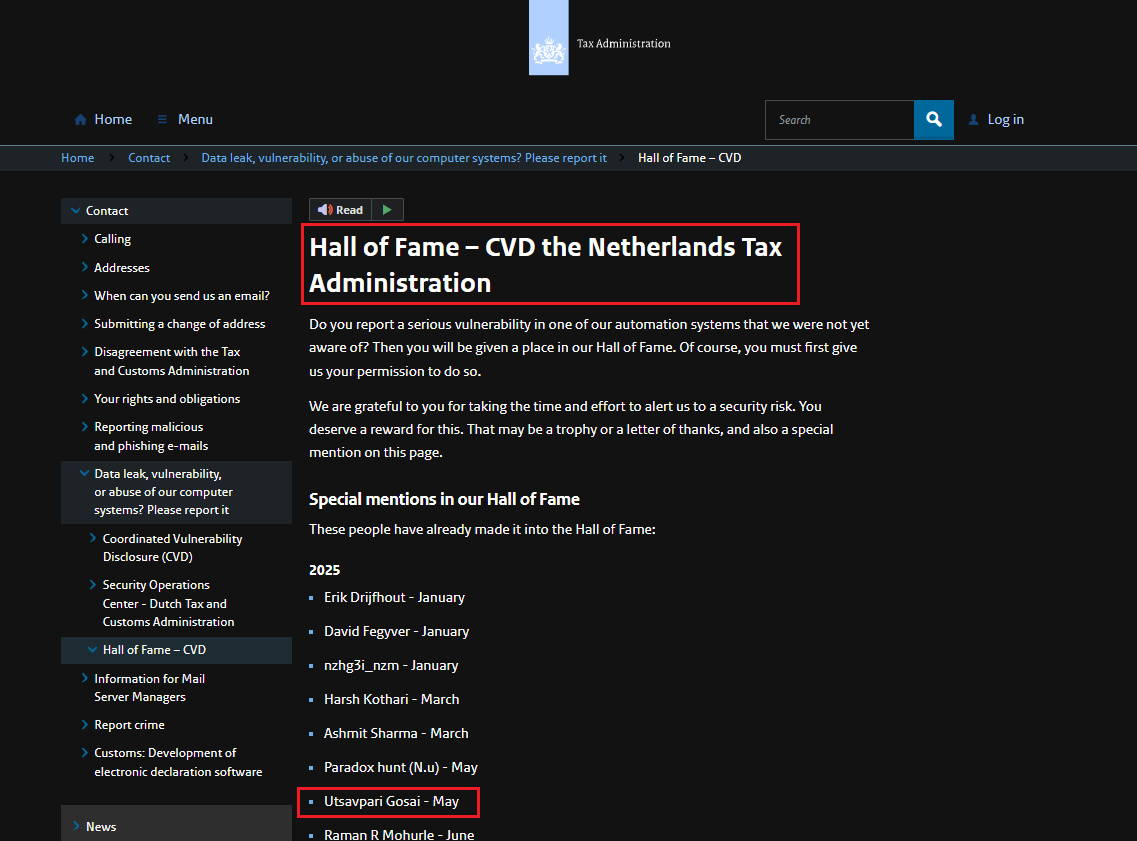
I was officially listed in the Hall of Fame 🏅 and received
a letter of appreciation from the Dutch Tax Authority! 📜🇳🇱
Hall Of Fame:
Here
💭 My Feelings
Despite thousands of researchers constantly working on Dutch government assets, I managed to find something unique and got recognized! as i recognized already in Apple, Upstox, HostGator, NASA (Government Of USA), Government Of India etc.....🌟
You can read that Articles in detail by clicking Back To Homepage button.
I thank God, my best friend, my friends, family, and all of you for supporting me in this journey. ❤️
💬 Need Help?
If you have any doubts, questions, or need guidance, feel free to reach out via my Linktree I’m here to help! 🤝💻
Thank you for reading! Stay ethical, stay sharp! 🔐👨💻
MR. X FACTOR
🔗 Handles:
- Linktree: https://linktr.ee/mrxfact0r_99