Hello Hackers,
It's been a while since we last connected! Life has been a bit of a whirlwind with my MCA exams and personal challenges. I even stepped away from my role as a Security Analyst (Penetration Tester) for personal reasons. These experiences taught me invaluable lessons especially about people, trust, and resilience.
But first, some good news! 🎉
I’m thrilled to share that I scored 100/100 in my MCA 3rd semester exams with a perfect 10.00 SGPA.
Currently, I’m in my final semester (4th), and things are looking bright. Now, let's dive into an
interesting story from my bug bounty journey.
The $25 Bounty Lesson 💰
About a year ago, as a beginner in bug bounty, I started applying my learning to real-world scenarios. I searched for bug bounty programs online using specific keywords. One day, I stumbled upon a WordPress website and tested a few endpoints:
https://target.nl/wp/wp-admin/upgrade.php
Vulnerability Description
When I accessed the install.php endpoint, I saw this message:
“Already Installed. You appear to have already installed WordPress. To reinstall, please clear
your old database tables first.”
Similarly, on upgrade.php, it displayed:
“No Update Required. Your WordPress database is already up to date!”
These messages exposed critical information about the site’s WordPress installation status and version.
Impact
This information, while seemingly harmless, could be exploited by attackers or automated tools to:
- Gather insights into the website’s infrastructure.
- Identify vulnerabilities tied to the specific WordPress version, increasing the risk of exploitation.
Outcome
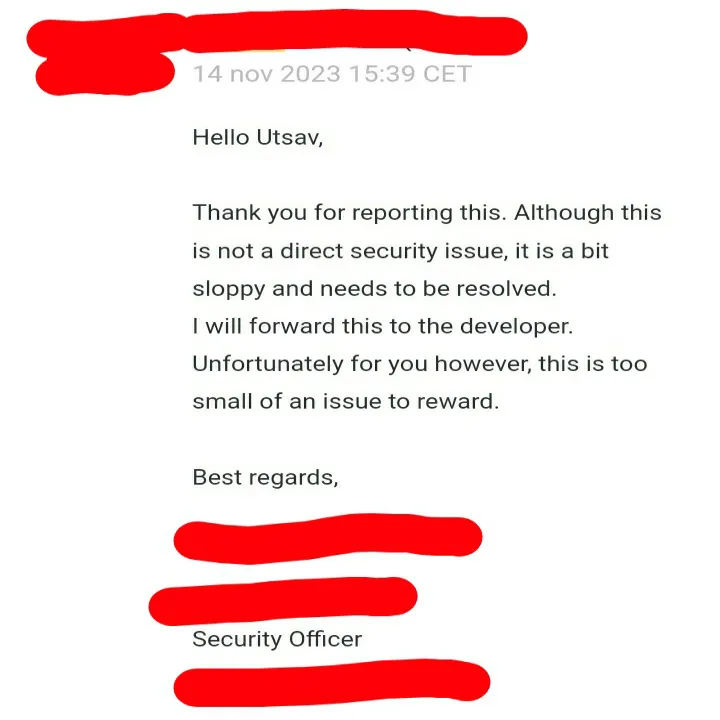
At the time, the company did not accept my report, labeling it as non-rewardable. I was disappointed but took it as a learning experience and moved on.
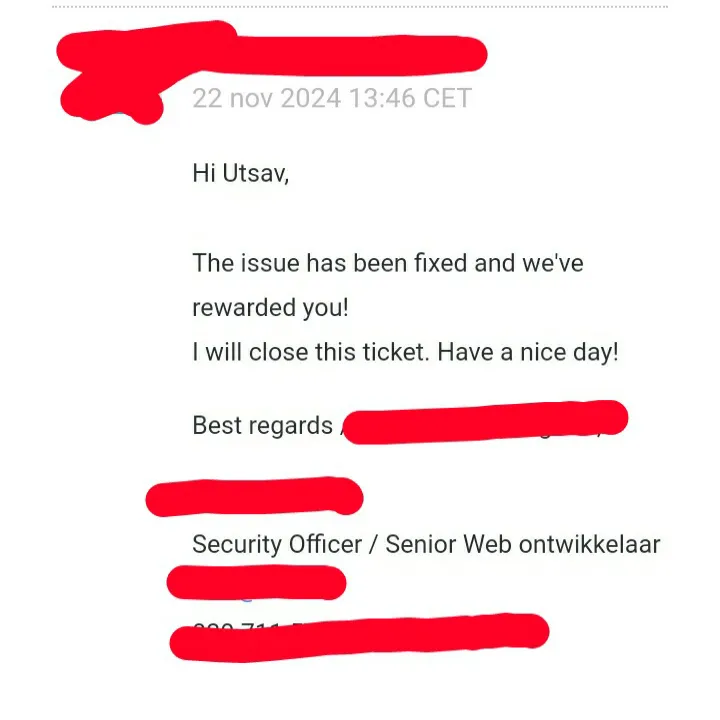
Fast forward one year I received an email from the same company. They informed me that my report was in triage mode, and their developers were working to fix it. Days later, they patched the bug and rewarded me with a small bounty of $25!
Even though the amount wasn’t huge, the experience taught me a powerful lesson:
"Never lose hope. Trust in your work, and have faith in your efforts. Results will come, even if
delayed."
A High-Impact Bug Awaiting Justice 🚨
Another memorable experience involved reporting a high-impact vulnerability (account takeover without user interaction) to a major company. Their bug bounty program promised rewards ranging from $700–$1000 for such findings.
Here is the link about that article:
Article
I reported the bug, emailed their team, and even contacted the site owner but received no response. Despite the frustration, I remain hopeful that they’ll acknowledge my report someday. If not, I trust my efforts will be rewarded elsewhere.
Key Takeaways
- Don’t Lose Hope ✨
Whether it’s a delayed response or no response at all, trust in your journey. - Trust Your Skills 💻
Every report, whether acknowledged or not, is a step toward mastering your craft. - Have Faith in the Process 🙏
Sometimes, results come unexpectedly just like my $25 bounty from a report I submitted a year ago.
That’s all for today! Let’s meet again soon with more exciting stories and lessons from the world of hacking.
Until then, Keep Hacking, Stay Secure! 🔐
Thank you for reading!
MR. X FACTOR
🔗 Handles:
- Linktree: https://linktr.ee/mrxfact0r_99