Hello Hackers! 👋
I hope you are all doing well and continuing to make the digital world a safer place. 🔐 Let's get started!
Today, I would like to share how I earned a total bug bounty of $50 ($25 + $25) by responsibly reporting two different security misconfigurations. Although the rewards were small, the experience taught me an important lesson about patience and persistence in bug bounty hunting.
🛡️ 1. Forced Logout via GET Request
The first issue involved a Forced Logout via a GET Request.
The application allowed users to be logged out simply by visiting a specific URL. No CSRF token or additional verification was required. This meant an attacker could send the logout URL to a victim, causing the victim to be logged out immediately.
Initially, the security team responded with:
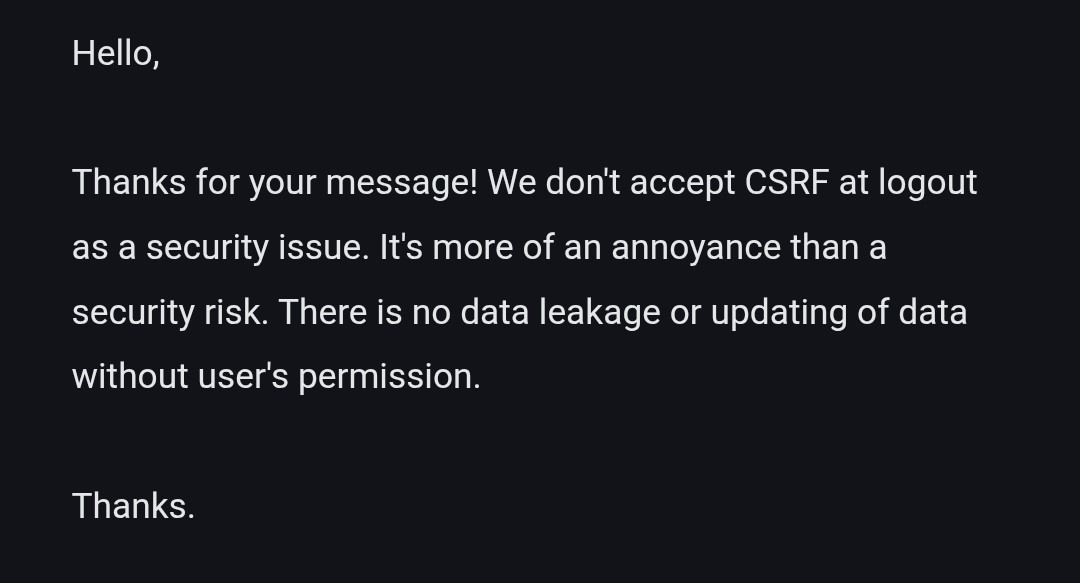
"We don't accept CSRF at logout as a security issue."
I clarified that my report was not a traditional CSRF vulnerability, but rather a security misconfiguration that allowed forced logout through a simple GET request without any user interaction or protection.
To be honest, after several months I almost forgot about the report. However, after approximately five months, I finally received an email saying:
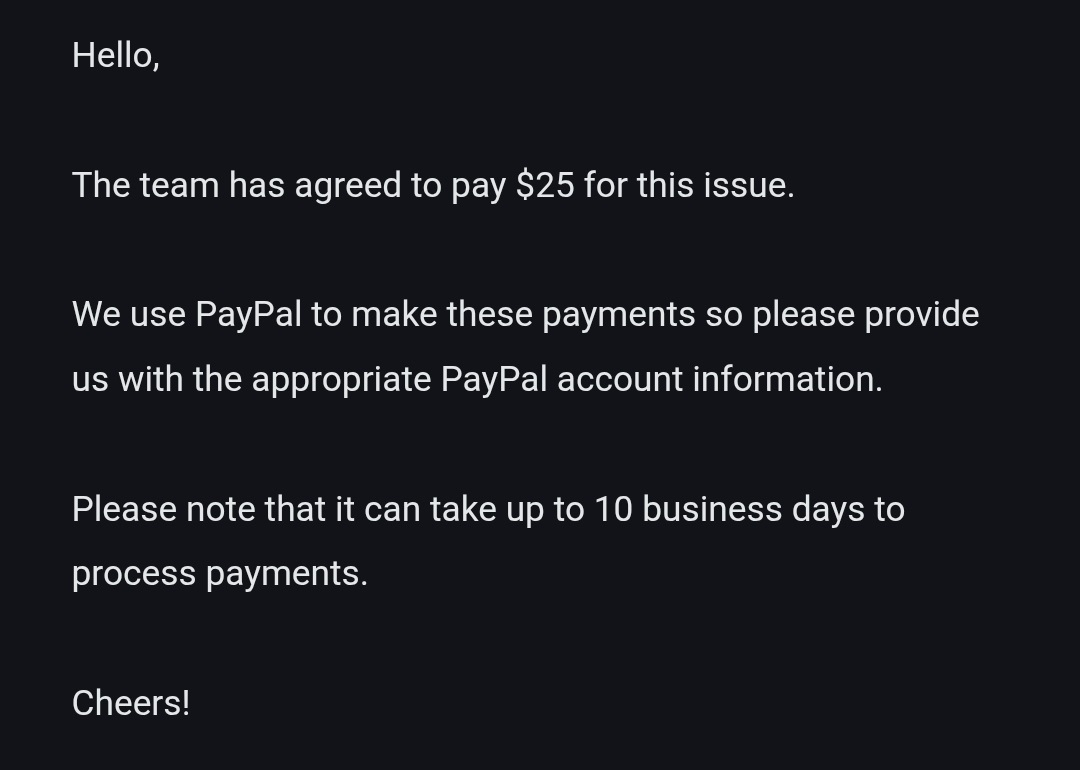
"Hello, The team has agreed to pay $25 for this issue."
🎉 Persistence paid off. The team eventually acknowledged the impact and rewarded me with $25.
💉 2. Injection Vulnerability
The second finding was an Injection vulnerability.
The application reflected my supplied input directly on the user's screen without proper sanitization. Improper handling of user-controlled input can introduce unnecessary security risks and should always be addressed through proper validation and output encoding.
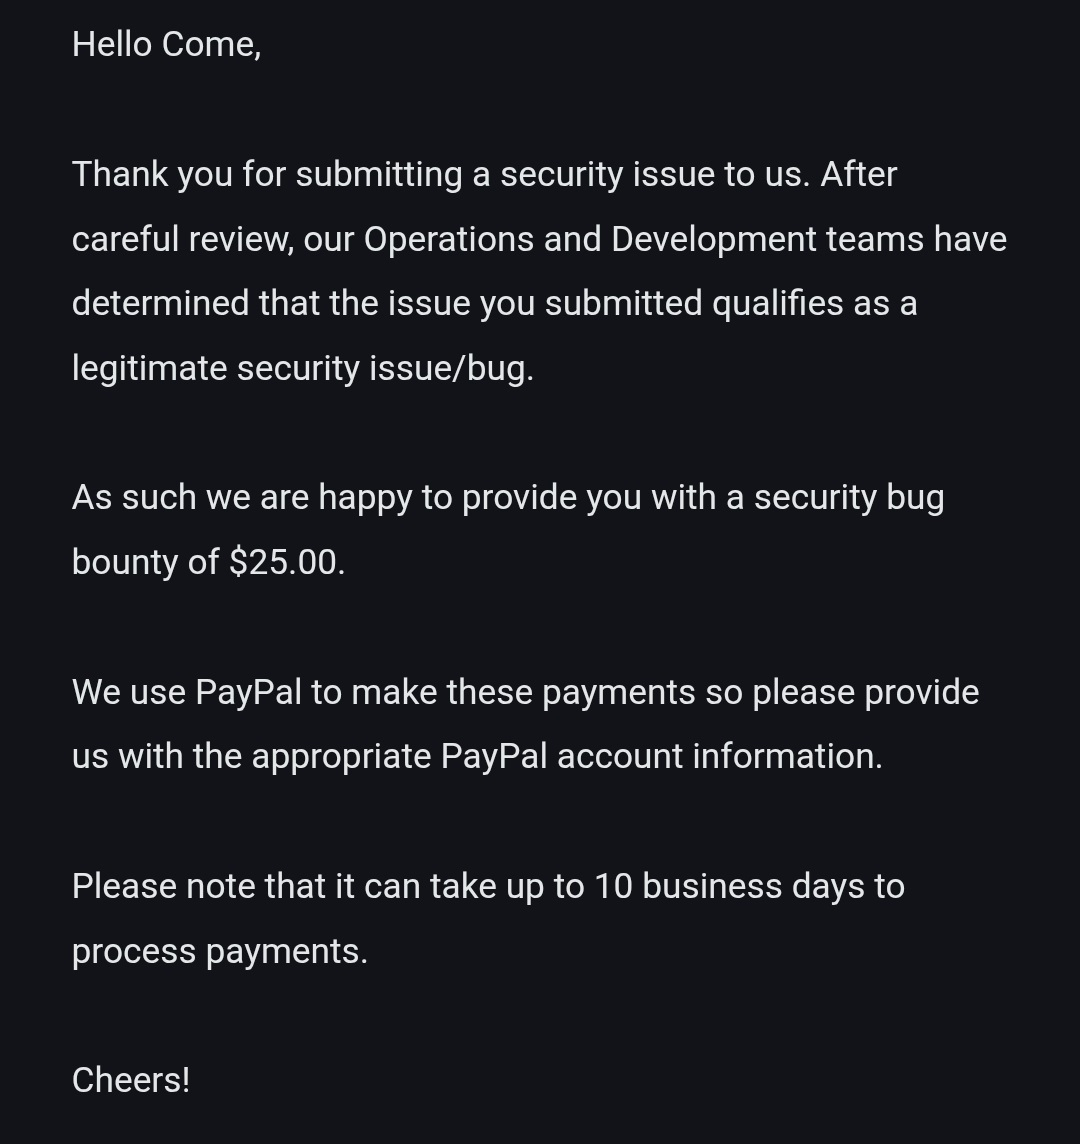
After reviewing and validating my report, the company rewarded me with another $25. 💰
🏅 Lessons Learned
- 🔍 Small security misconfigurations can still have real security impact.
- 🛡️ Never underestimate seemingly low-severity findings.
- 📩 Clear communication with security teams is just as important as finding the bug.
- ⏳ Patience is a key skill in bug bounty hunting.
- 🚀 Keep learning, keep reporting, and never stop improving.
💡 Final Thoughts
Sometimes, God tests your patience not only in bug bounty hunting but also in life.
Never give up. Never stop learning. Never stop hunting.
✨ Miracles can happen at any time, so keep reporting, keep improving, and stay patient.
If you have any questions or would like to connect, feel free to reach out through my Linktree or social media handles.
Thank You
MR.X FACTOR
🔗 Handles:
- Linktree: https://linktr.ee/mrxfact0r_99