Hello Hackers 👋
I hope you are all doing well and continuing to make the digital world a safer place through your security research and responsible disclosure efforts 🔐💻
Today, I would like to share an exciting experience from my bug hunting journey.
🇷🇺 An Unexpected Discovery
As many of you may know, the Russian Government does not publicly operate a bug bounty program. Based on my research, only security researchers and bug hunters from Russia are generally permitted to test and report vulnerabilities on their systems.
However, while conducting security research, I discovered an information disclosure issue on a Russian Government website 🌐⚠️
The issue exposed information that should not have been publicly accessible and could potentially provide useful intelligence to malicious actors.
Since I have previously helped secure assets belonging to organizations and government entities such as USA (NASA), the Netherlands Governmentv(Dutch Gov.), and various Indian Government departments, I felt a responsibility to report the issue through the proper channels.
⚖️ Responsible Disclosure
Before submitting the report, I carefully explained that I had not exploited the vulnerability in any way.
I also stated that I fully respect the cyber laws and regulations of countries such as Russia, China, Japan, and other nations that maintain strict policies regarding unauthorized security testing and cannot allow other country's hackers to hunting on his websites
My intention was not to test beyond what was necessary to verify the issue, but simply to help improve security through responsible disclosure.
After preparing a detailed report, I submitted the information to the relevant contact point and waited for a response 📧
📩 The Response
To my surprise, I received a reply from their security team.
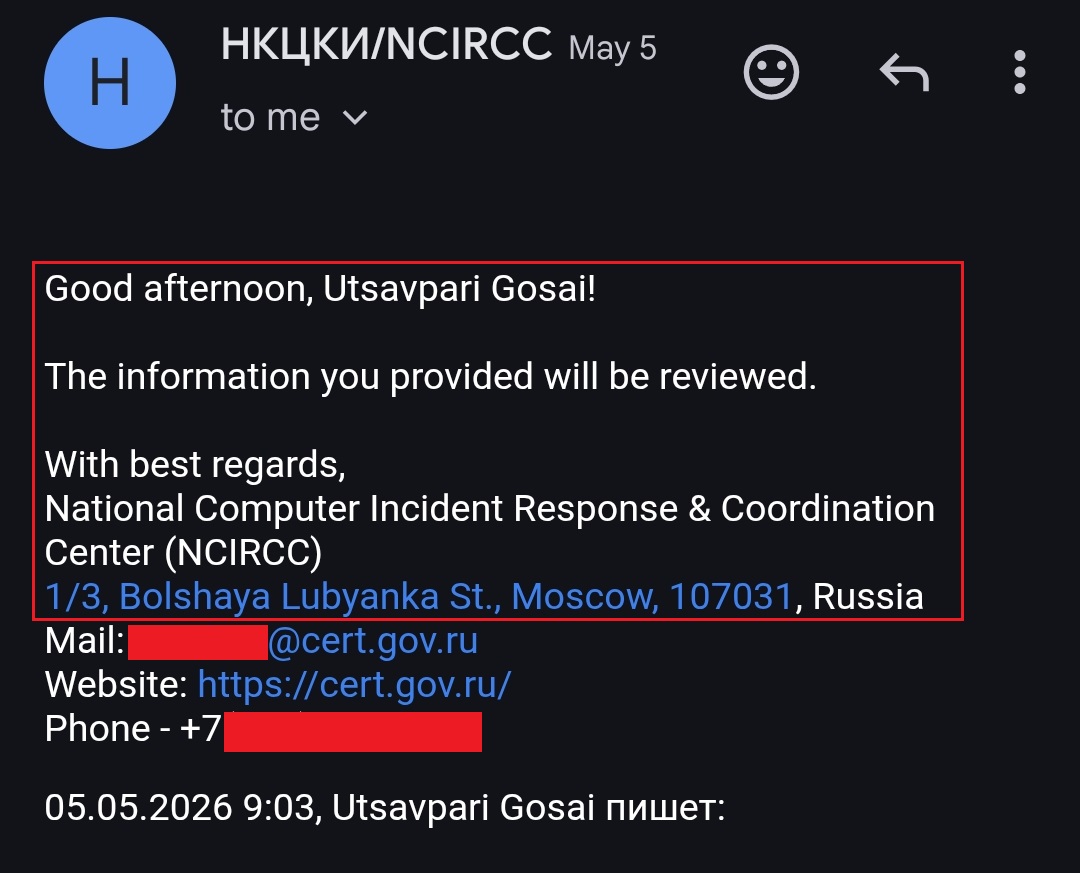
They thanked me for reporting the issue and informed me that the details had been forwarded to the relevant team for review and remediation ✅🎉
Receiving an acknowledgment from a Russian Government entity was something I had never expected, especially considering the strict regulations surrounding security testing within the country.
🏅 Final Outcome
- ✅ Information disclosure issue identified
- 📧 Vulnerability reported responsibly
- ⚖️ Respect for local cyber laws clearly communicated
- 📩 Official response received from the security team
- 🔧 Issue forwarded for review and remediation
- 🏆 Acknowledgment received from a Russian Government entity
💡 Final Thoughts
Experiences like these remind us that responsible disclosure can make a positive impact regardless of borders.
Security is a global responsibility, and every valid report contributes to making the internet safer for everyone 🌍🔒
I was extremely happy and honored to contribute to the security of one of India's long-standing strategic partners 🇮🇳🤝🇷🇺
Moments like these motivate me to continue helping organizations and governments strengthen their security posture through ethical research and responsible disclosure.
Thank you, God, for giving me this opportunity 🙏
If you have any questions or would like to connect, feel free to reach out through my Linktree and social media handles 📱✨
Thank You,
MR. X FACTOR
🔗 Handles:
- Linktree: https://linktr.ee/mrxfact0r_99