Hello Hackers! 👨💻🔥
I hope you are all doing well and continuing to help secure our digital landscape 🌍🔐
Today, I want to share how I discovered a security issue on HP's website and received an acknowledgment from their security team 🏆💙
As an HP Victus gaming laptop user, receiving recognition from a company whose products I use personally was a very special moment for me 😊
🚀 The Discovery
During my bug-hunting journey, I was performing reconnaissance and content discovery on one of HP's web applications 🔍⚡
While testing the target, I used a custom wordlist that I created through my own research and reconnaissance efforts 🛠️
After performing enumeration, I discovered a publicly accessible .php file containing sensitive installation-related information 🚨
⚠️ Security Impact
The information exposed within the file should not have been publicly available and could potentially assist attackers in understanding internal application configurations 🔓
Exposed installation files and configuration-related resources often reveal sensitive details that can increase an application's attack surface ⚠️
📩 Responsible Disclosure
After validating the finding, I responsibly reported the issue to HP through their official security disclosure email 📧🛡️ found at here: https://enable.hp.com/potentialsecurityvulnerability-report
The HP security team reviewed the report and worked to remediate the issue ✅
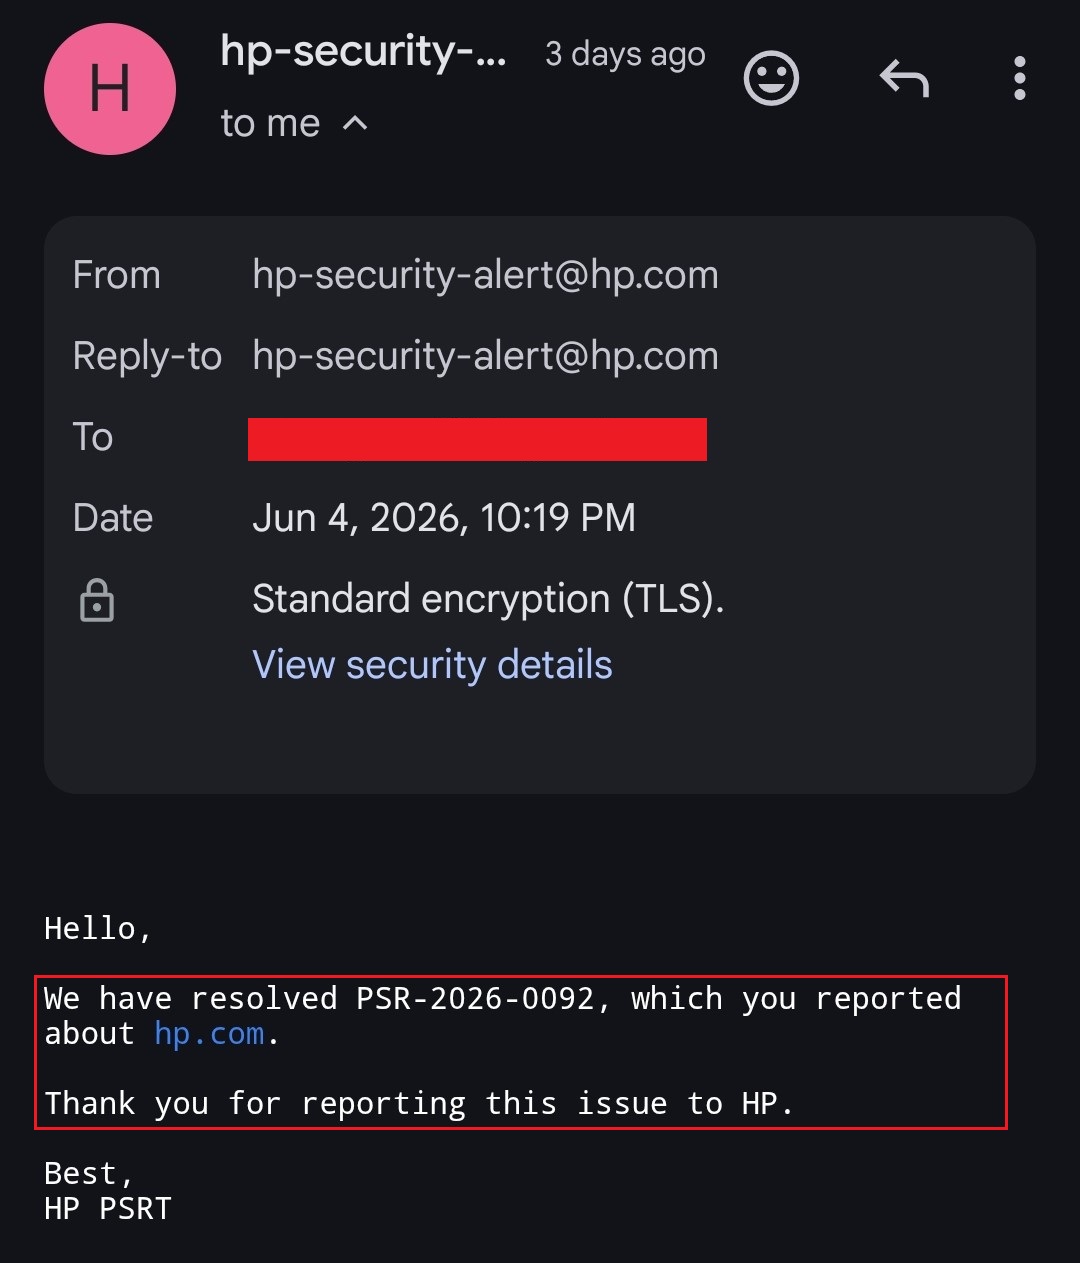
After the fix was implemented, they confirmed the resolution and acknowledged my contribution toward improving the security of their platform 🎖️🎉
🏅 Key Takeaways
- 🔍 Reconnaissance is one of the most important phases of bug hunting
- 🛠️ Custom wordlists can help uncover hidden assets and endpoints
- 📂 Misconfigured installation files can expose sensitive information
- 📩 Responsible disclosure helps organizations improve security
- 🚀 Consistent learning and testing can lead to valuable findings
💡 Advice for Hunters
Never underestimate simple misconfigurations during reconnaissance 👀
Sometimes a seemingly small exposed file can reveal valuable information and lead to impactful security findings 🔥
🧠 Final Thoughts
Receiving acknowledgment from HP was a great experience and motivated me to continue learning, researching, and contributing to cybersecurity 💻🛡️
Every finding, no matter how small it may seem, contributes toward making the internet a safer place 🌍🔐
If you have any questions or would like to connect, feel free to reach out through my Linktree profile 🔗
Thank You,
MR. X FACTOR 😎
🔗 Handles:
- Linktree: https://linktr.ee/mrxfact0r_99