Hello Hackers 👨💻🔥
I hope you all are doing well and continuing to secure our digital world 🌍🔐
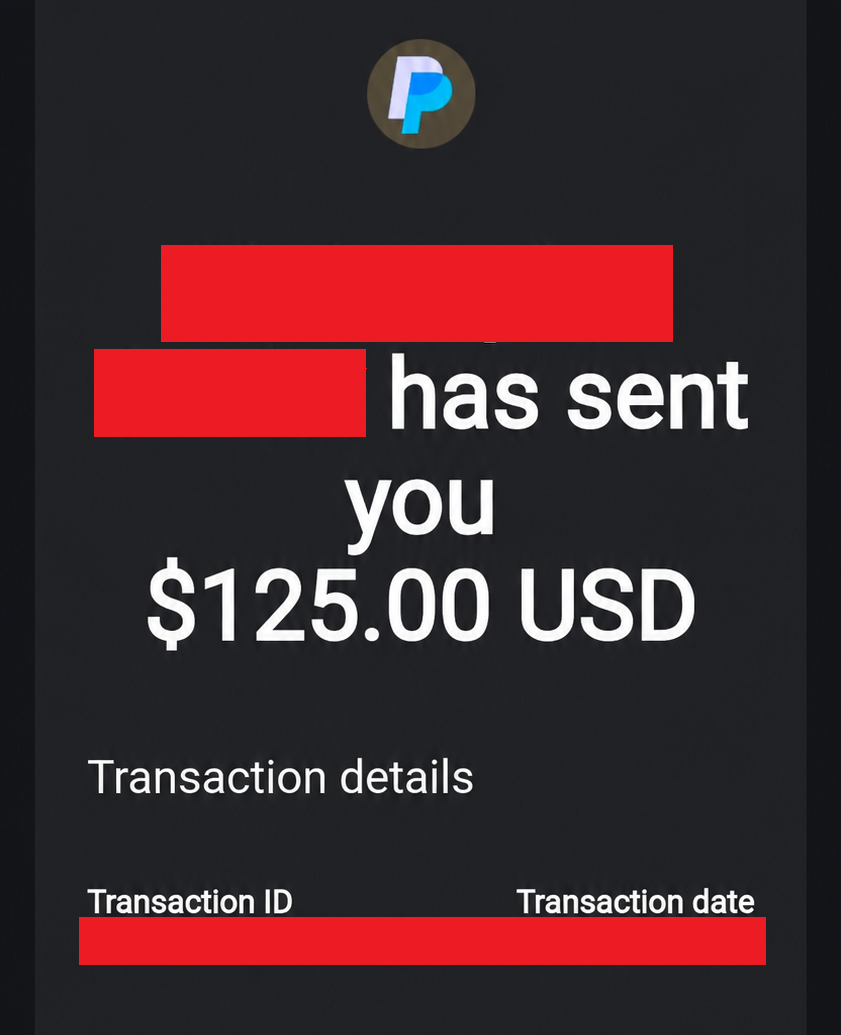
Today, I want to share how I earned a $125 bounty 💰🚀
🚀 The Journey
During my testing and reconnaissance process, I discovered multiple vulnerabilities 🔍🐛
Some of the reported issues are still under the patching process, so I cannot disclose full technical details yet 🤫
💉 Injection Vulnerability
One of the vulnerabilities I discovered was an Injection Vulnerability 💉
This issue had the potential to impact backend functionality and expose sensitive behavior within the application ⚠️
📂 Sensitive Information Disclosure
Another issue involved a Sensitive Information Disclosure caused by a leaked .json file 📂
I discovered this file using my custom wordlist during content discovery and endpoint enumeration 🛠️
Misconfigured or exposed files can unintentionally leak internal information and create additional attack surfaces 🔓
📩 Responsible Disclosure
After verifying the vulnerabilities, I responsibly reported them to the affected organization 📩
The security team reviewed the findings and rewarded me with a $125 bounty 💰✅
🏅 Key Takeaways
- 🔍 Recon and content discovery are extremely important
- 📂 Exposed files can reveal sensitive information
- 💉 Injection vulnerabilities still exist in modern applications
- 🛠️ Custom wordlists can help uncover hidden assets
- 📩 Always follow responsible disclosure practices
💡 Small Tip For Hunters
Never ignore uncommon file extensions during recon 👀
Sometimes leaked .json, backup, or configuration files can expose valuable information that leads to bigger findings 🔥
🧠 Final Thoughts
Keep learning, keep securing, and keep hacking ethically 🧠💻🛡️
Every small finding can lead to something bigger if you stay consistent and curious 🚀
If you have any questions or queries, feel free to contact me through the Linktree link in the description 🔗
Thank You,
MR.X FACTOR 😎
🔗 Handles:
- Linktree: https://linktr.ee/mrxfact0r_99