Hello Hackers 👨💻👩💻
I hope you’re all doing well and continuing to secure our digital world 🌍🔐
Today, I’m excited to share my journey of earning a Hall of Fame recognition from McDonald’s through Bugcrowd 🍟🍔
🔍 Getting Started
McDonald’s runs a Vulnerability Disclosure Program (VDP) on Bugcrowd, so I started with reconnaissance by gathering subdomains of their domain.
I used GoWitness 📸 to capture screenshots of all discovered subdomains and began reviewing them one by one.
🧪 The Discovery
During my exploration, I found a login page 🔐. Initially, testing didn’t reveal anything critical.
However, while analyzing the forgot password functionality, I discovered a username enumeration vulnerability.
The issue was:
- ⚠️ The application revealed whether a user account exists
- ❌ It showed different responses for valid and invalid users
- ✅ Instead of using a generic response like “If the account exists, you will receive an OTP”
⚠️ Impact
Although classified as a low-severity vulnerability, this issue can help attackers identify valid user accounts.
Such information can be leveraged in further attacks like brute force or phishing campaigns.
As a security researcher 🛡️, I strongly believe:
Every vulnerability matters — from informational (P5) to critical (P1)
Even small issues can become dangerous when chained together 🔗💥
📩 Reporting
I responsibly reported the vulnerability through Bugcrowd without exploiting it.
- ✅ The report was accepted as Low Severity
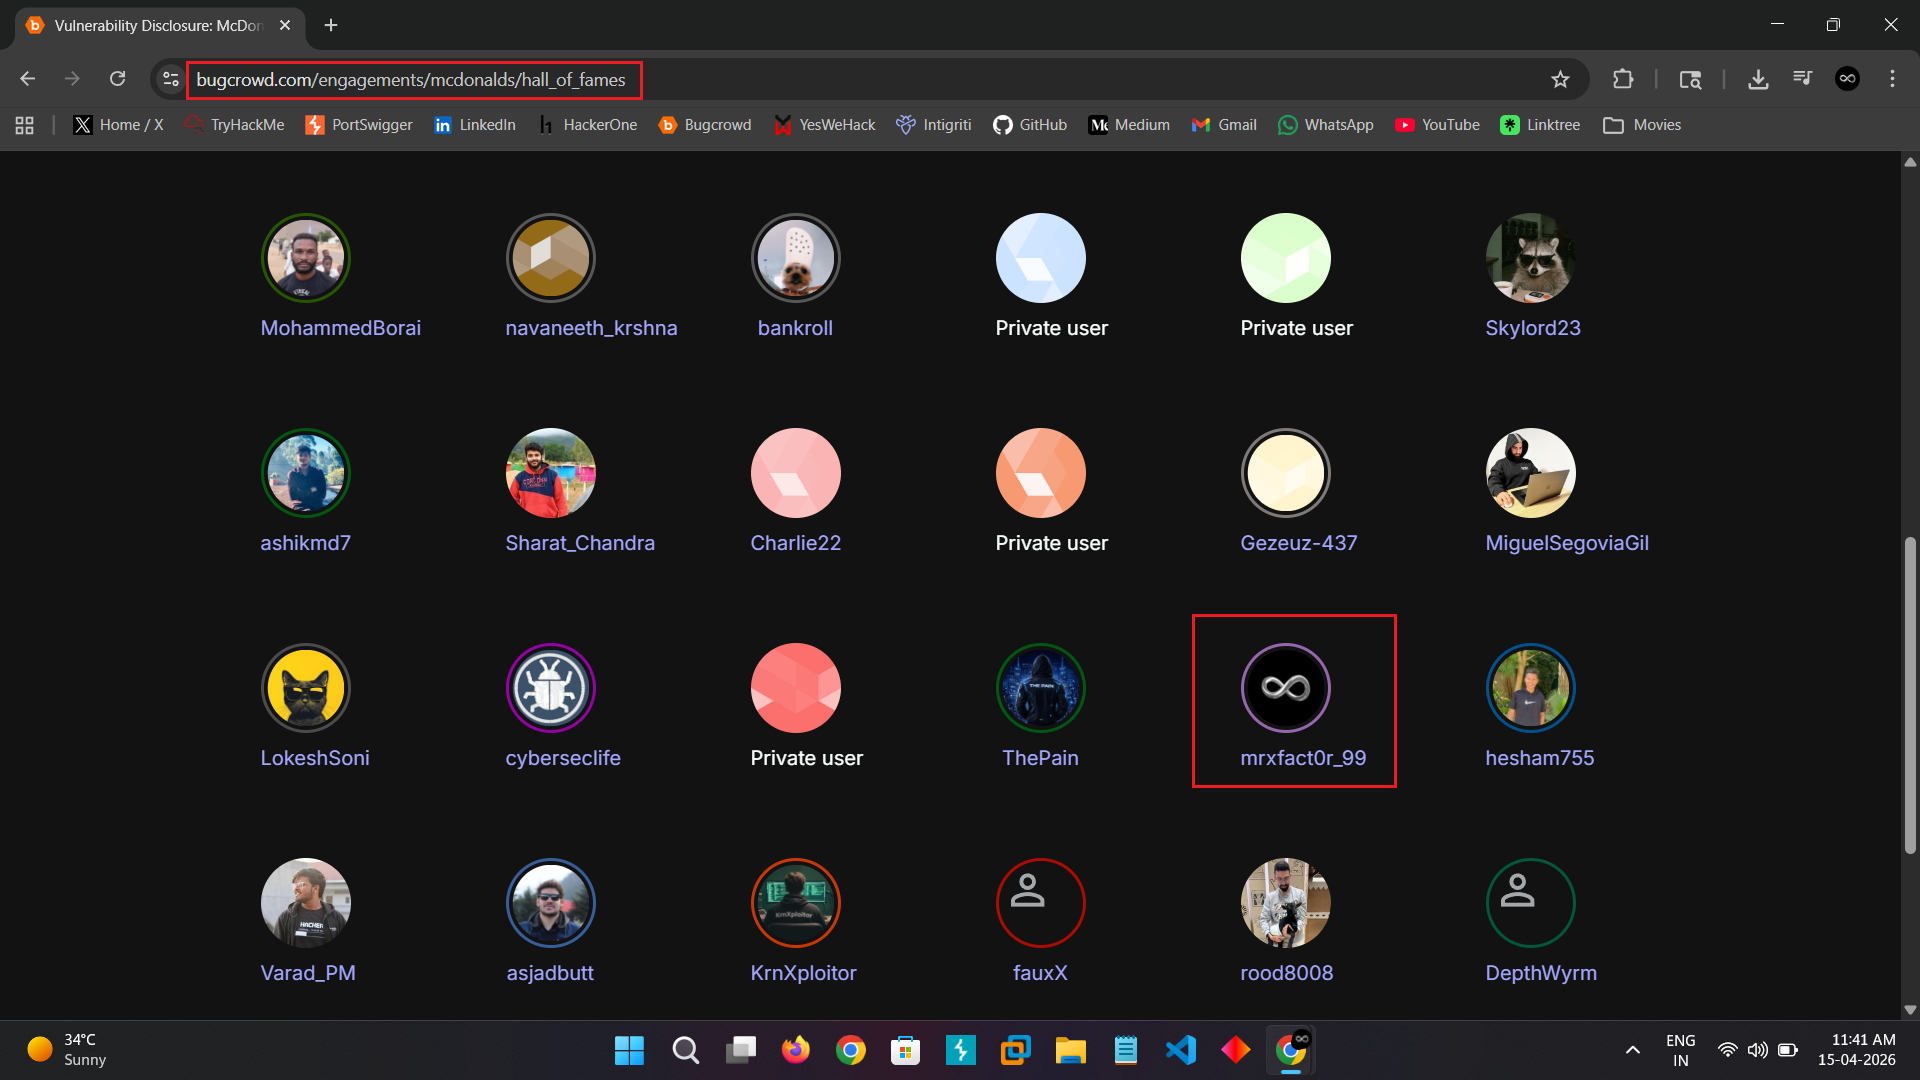
- 🏅 I received a Hall of Fame recognition
- Hall Of Fame: https://bugcrowd.com/engagements/mcdonalds/hall_of_fames
💡 Final Thoughts
Always remember:
- 🚪 No finding is too small
- 🔍 Even minor issues can lead to major risks
- 🌐 Responsible disclosure makes the internet safer
If you found this helpful or learned something new, feel free to reach out 🙌
Thank You,
MR. X FACTOR 🚀
🔗 Handles:
- Linktree: https://linktr.ee/mrxfact0r_99