Hello Hackers 👋🔐
I hope you’re all doing well and continuing to secure our digital landscape 🔐💻
Today, I want to share how I discovered a security vulnerability in Rapido and responsibly disclosed it to their team 🚕⚡
🔍 The Discovery
While casually exploring Rapido’s website, my curiosity as a security researcher and ethical hacker kicked in 🤔. During my testing, I came across a subdomain and decided to perform directory brute-forcing.
During this process, I discovered a configuration file that exposed sensitive information such as:
- 🚨 API Keys
- 🔑 Tokens
- 🛠️ Credentials
This was a serious case of:
- ⚠️ Sensitive Information Disclosure
- ⚙️ Security Misconfiguration
Since the issue is currently being fixed, I won’t disclose specific technical details or file names.
🏢 Responsible Disclosure
As an ethical hacker and bug bounty hunter, I immediately reported the vulnerability responsibly to the Rapido team without exploiting the issue.
Responsible disclosure is a crucial part of ethical hacking our goal is always to protect users and strengthen systems, not misuse vulnerabilities 🔒
✅ Response & Acknowledgment
After submitting the report, I was genuinely happy to receive acknowledgment from the Rapido team 🙌
In many cases especially in India 🇮🇳 companies silently fix vulnerabilities, mark reports as duplicates, or sometimes don’t even respond.
However, Rapido stood out. Despite not having a public bug bounty program, their team appreciated the report and is actively working on fixing the issue 💯
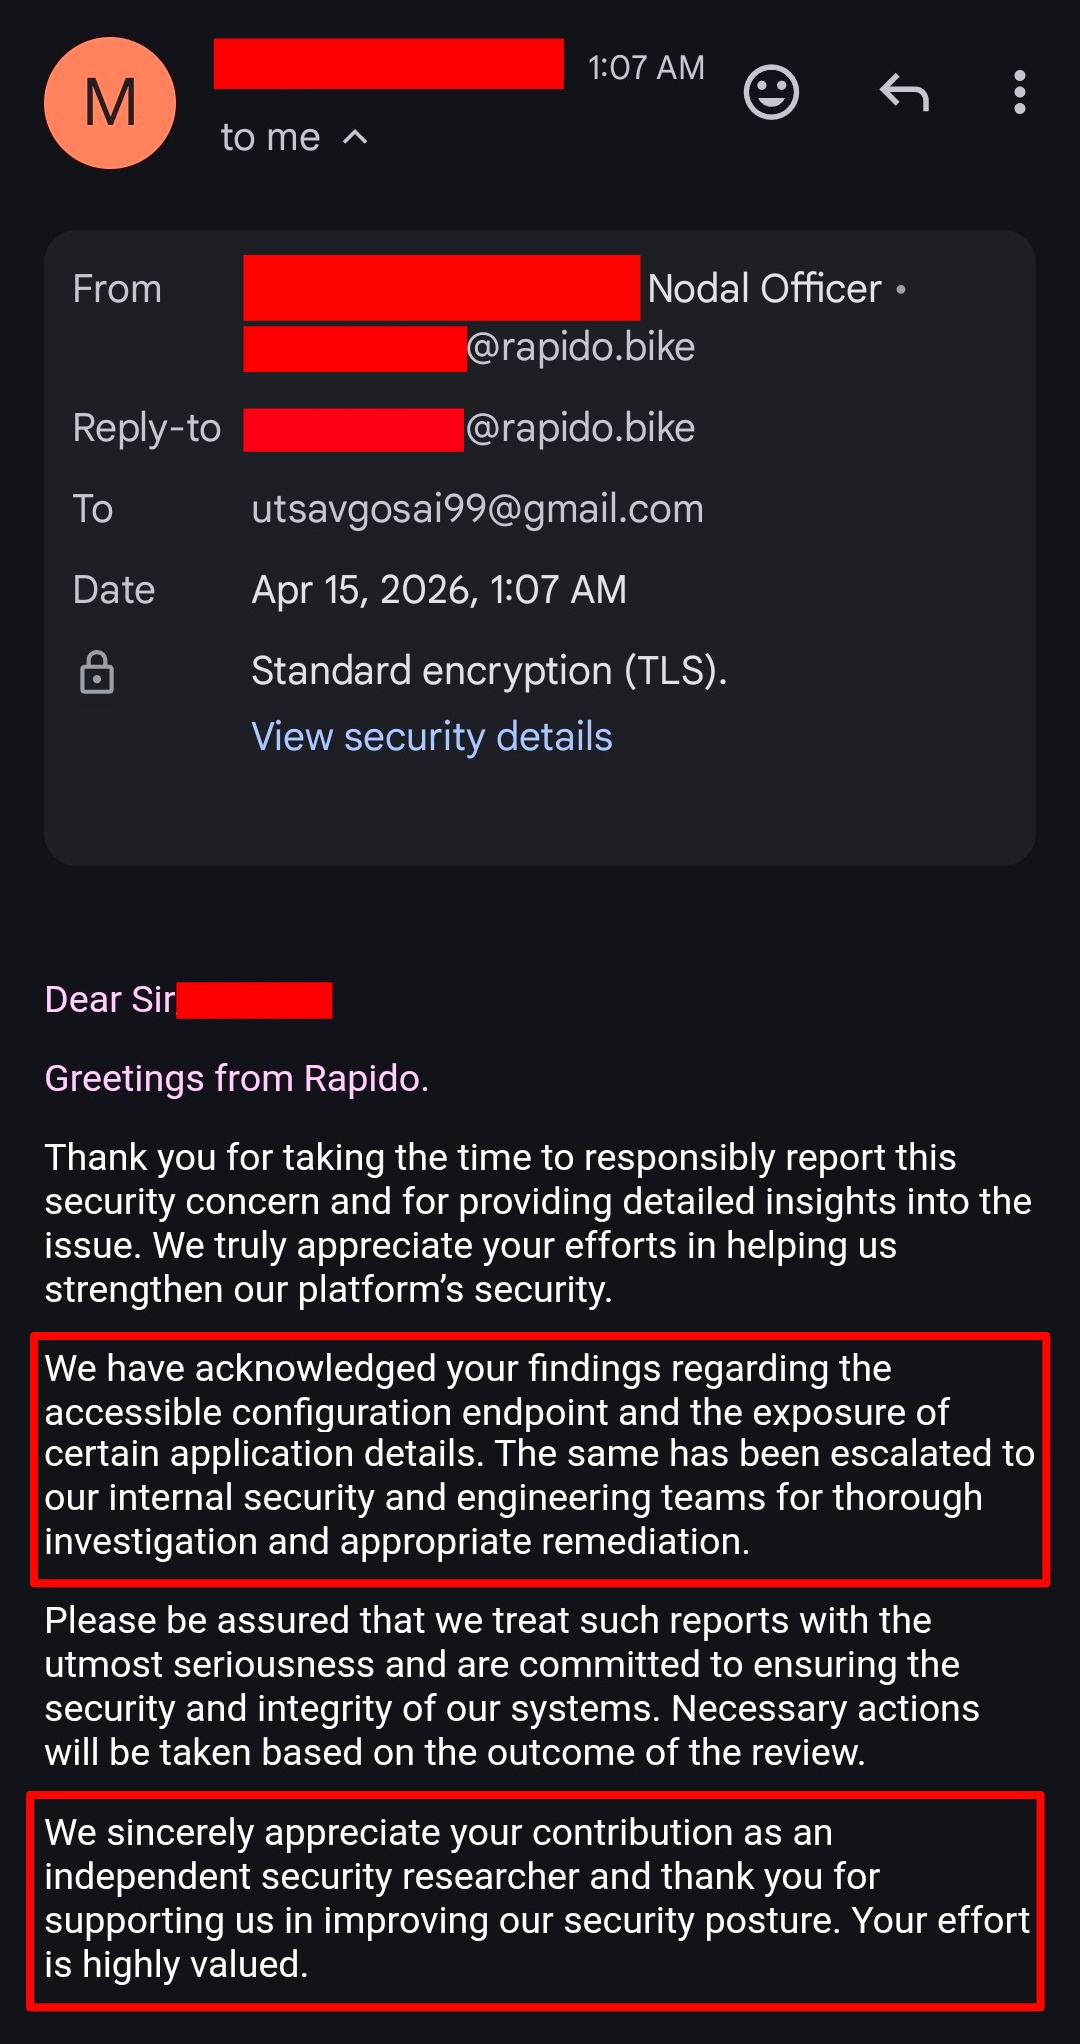
This reflects their professionalism and shows how seriously they take user data protection and digital security 🔐
🛡️ Final Thoughts
Always follow ethical hacking principles. If you discover a vulnerability, report it responsibly and give the organization time to fix it.
Together, we can make the internet a safer place 🌍🔐
If you have any questions or queries, feel free to reach out via the link in the description 📩
Thank You,
MR. X FACTOR ✨
🔗 Handles:
- Linktree: https://linktr.ee/mrxfact0r_99