Hello Hackers 👨💻
I hope you all are doing well and continuing to secure our digital landscape 🌐🔐
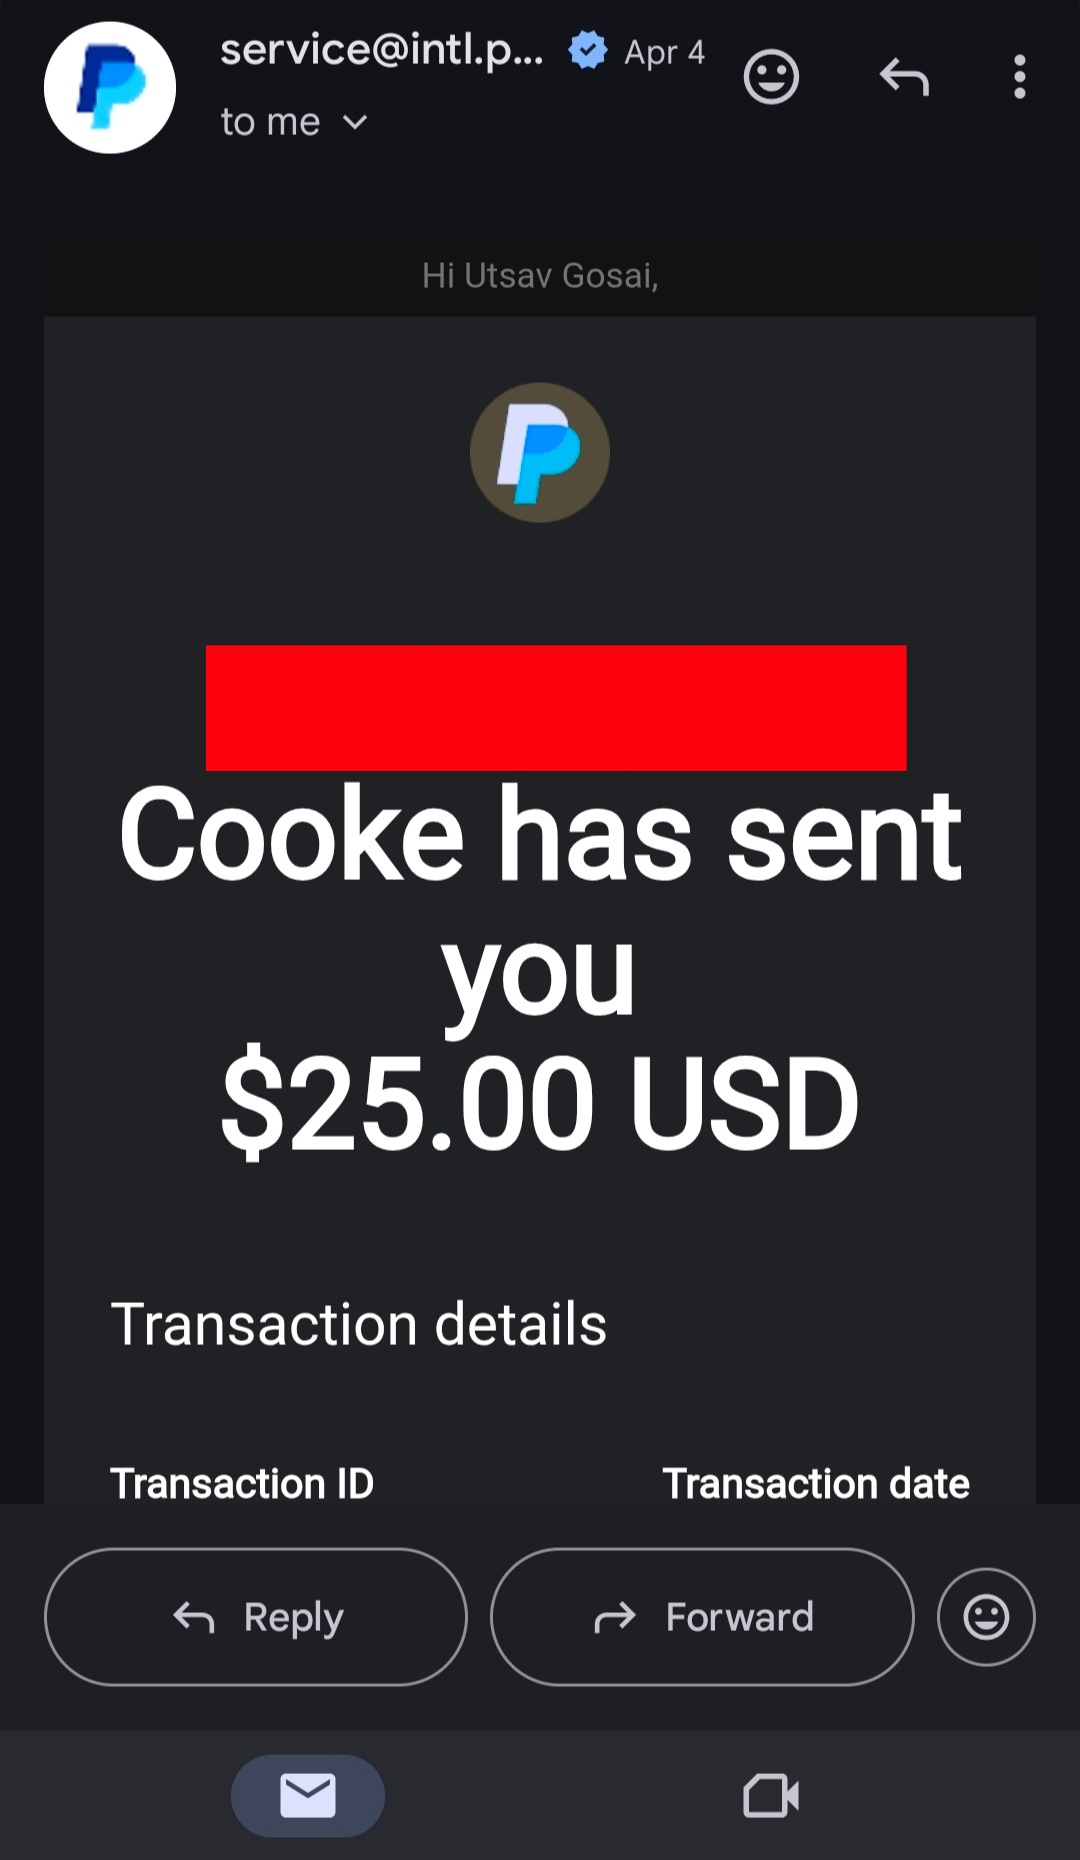
Today, I’m introducing a unique challenge with a $25 bounty 💰 for identifying an Email Injection vulnerability related to improper input validation ✉️⚠️
🔍 What is Email Injection?
In some web applications, user inputs like email or username are passed through URL parameters (GET requests). If these inputs are not properly validated or sanitized, attackers can manipulate them to inject malicious values.
This type of issue is commonly referred to as Email Injection, and it can lead to unexpected behavior, data exposure, or even account compromise 🚨
⚠️ Where Does the Problem Occur?
Many applications still rely on sending sensitive data such as email and password through GET parameters. This creates a risk because:
- 🔗 URLs can be easily modified by attackers
- 📤 Sensitive data may be exposed in browser history or logs
- ⚠️ Improper validation can allow injection of malicious payloads
🧠 Challenge Objective
Your goal is to identify and demonstrate a meaningful impact using Email Injection techniques. Think creatively and explore how improper input handling can be exploited in real-world scenarios.
🛠️ Tips for Finding the Issue
- 🔍 Look for parameters like
?email=or?username=in URLs - ✏️ Try modifying parameter values manually
- 🧪 Test for input validation weaknesses
- 🧠 Analyze how the application processes user input
Always follow ethical hacking practices. Do not exploit vulnerabilities beyond proof-of-concept. The goal is to identify and report issues responsibly to improve security 🌍🔐
If you have any questions or queries, feel free to connect with me via DM links 📩
Thank You,
MR. X FACTOR 🚀
🔗 Handles:
- Linktree: https://linktr.ee/mrxfact0r_99