Hello Hackers,
I hope you all are fine and well. So first of all, sorry for not sharing any bug hunting stories recently. Because of holidays and vacations, I was busy enjoying time with family and friends, so no stories or articles were uploaded. But now the vacation is over, so it’s back to work! 💻🎯
I am going to share with you an interesting and commonly ignored type of bug today. So let’s get started! 🐞🔍
I began by analyzing the structure of the target web application. This step is very important and
often missed by many bug hunters. While exploring, I discovered a page named
SupportForm.aspx. It had input fields like name, email, your query, some other options,
and a submit button.
I usually start by sending a demo message to see how the form works. Then I tried sending blind SSRF and blind XSS payloads but nothing worked. I assumed there was no bug and thought about moving on.
But suddenly, while I was eating 🍽️, an idea hit me 💡 what happens if I submit the form using any random email address?
I tried it, and surprisingly, it got submitted and accepted successfully ✅.
Then I wondered why not try sending it using an admin or company email address? I used OSINT to find some company emails and submitted the form again. And guess what? It worked! The message was sent successfully using their internal email address. 📬
So what is the bug?
There’s a twist here. The form was:
- Accepting any email address, including internal or company ones.
This Means:
- Attackers can impersonate company employees or customers and submit misleading or malicious requests (like asking for password resets, admin access, or sensitive info).
- If internal teams respond to spoofed messages without verifying the sender, attackers might receive confidential information.
- Combined with user enumeration, attackers can target known employees or customers with social engineering.
- This seriously undermines the integrity of the support system. ⚠️
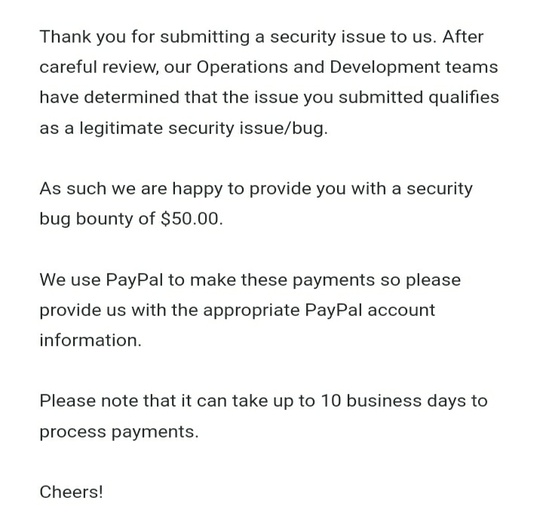
I reported it with this mindset, and the report was accepted in 10 days. I received a $50 reward. 🤑
The Takeaway: Bugs are everywhere you just need to think like an attacker or hacker. Understand how the company works, and you’ll find vulnerabilities that many others miss. 🧠💥
That’s all for today. Thank you for reading! If you have any questions or need help, feel free to reach out via the link below.
Thank You,
MR.X FACTOR 🚀
🔗 Handles:
- Linktree: https://linktr.ee/mrxfact0r_99