Hello, Hackers! 👨💻🔥
I hope you're all doing well! 🚀
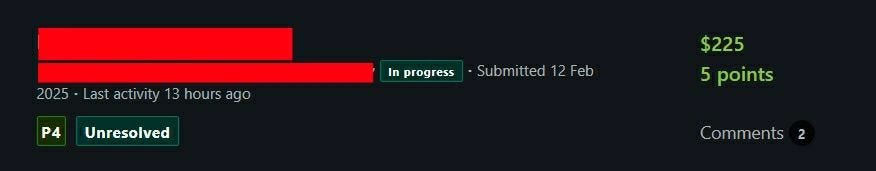
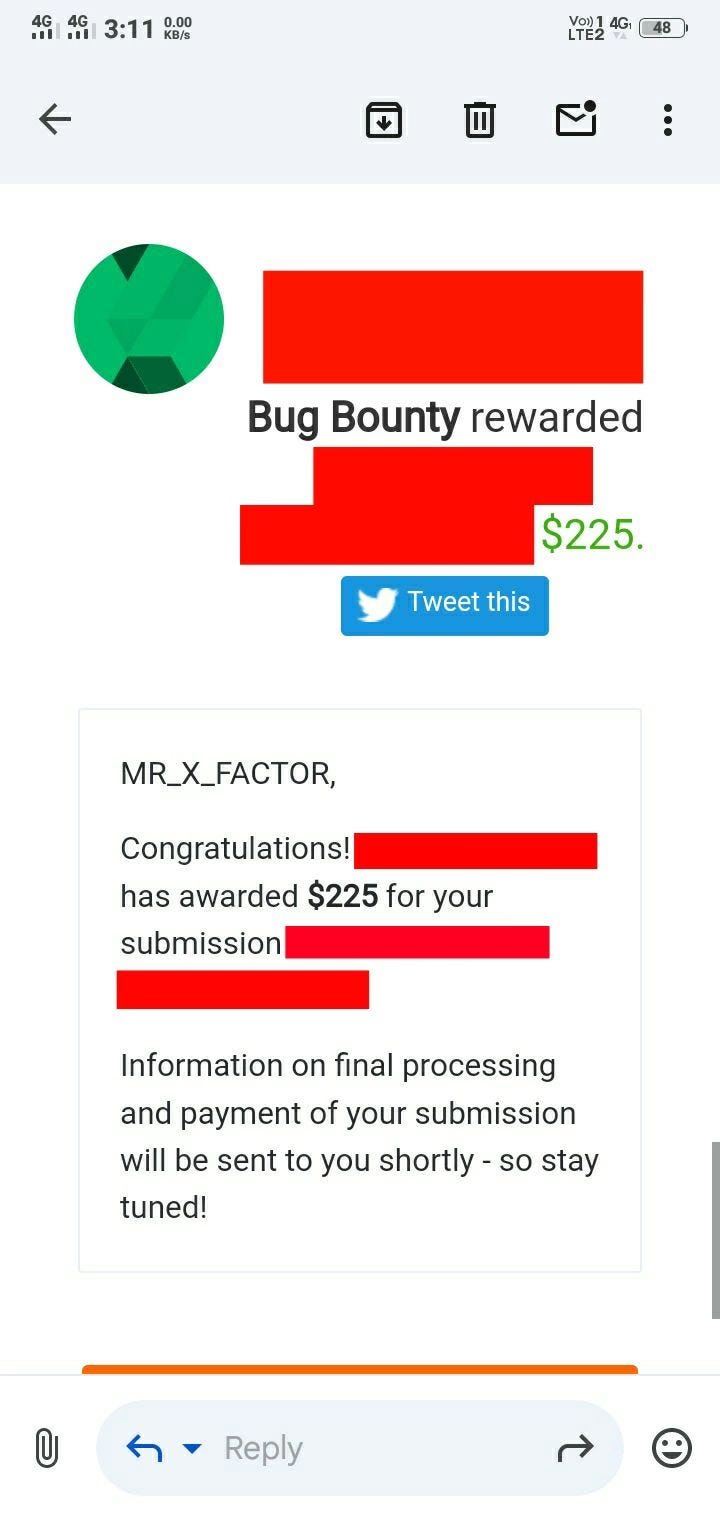
Today, I want to share my experience of finding a bug in a Bugcrowd program that earned me a $225 bounty, 5 points, and a spot in the Hall of Fame! 🏆💰
The Challenge
Platforms like HackerOne and Bugcrowd are now packed with security researchers. This makes the chances of getting informative, N/A, or duplicate reports much higher. So, whenever you find a valid bug, it becomes even more valuable! 💎
Recently, I found several valid bugs, and I was thrilled about it. However, due to Bugcrowd's policies, I can't disclose the full details of the bug. I've already been warned before, so I need to be cautious.
But I can still share a tip to help you in your bug hunting! 🕵️♂️
💡 Bug Hunting Tip
If a website uses WordPress in the backend, you can use this wordlist:
This can help you discover some interesting P2–P4 bugs! 🔍🐞
I hope this tip helps you in your bug bounty and security journey! 💻🚀
If you have any questions or need help, feel free to ping me on my handles below! 👇
Thank You! 🙌
MR.X FACTOR