Hello Hackers,
I hope this message finds you all safe, well, and actively contributing to making the digital world more secure! Let’s dive right into today’s story it’s a short but valuable lesson for all bug bounty hunters out there.
The $50 Recheck Bounty 💵
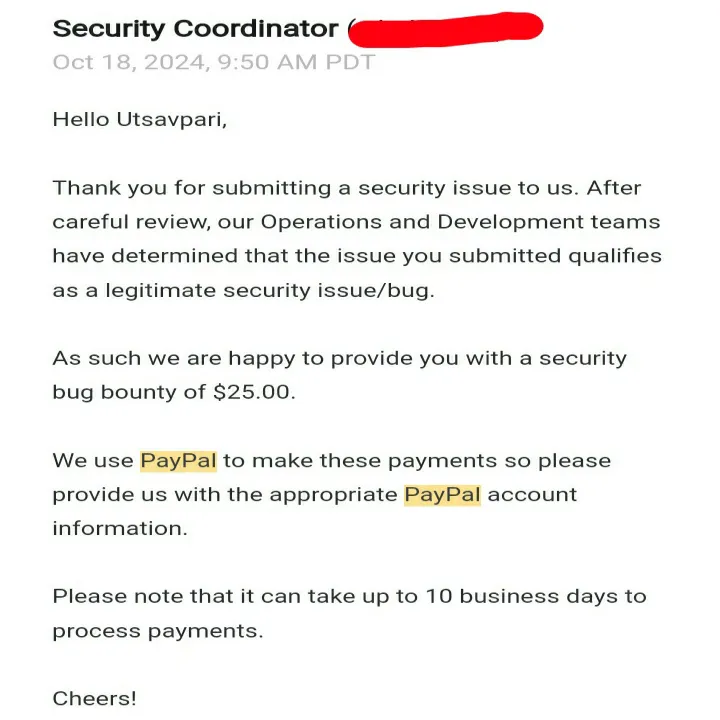
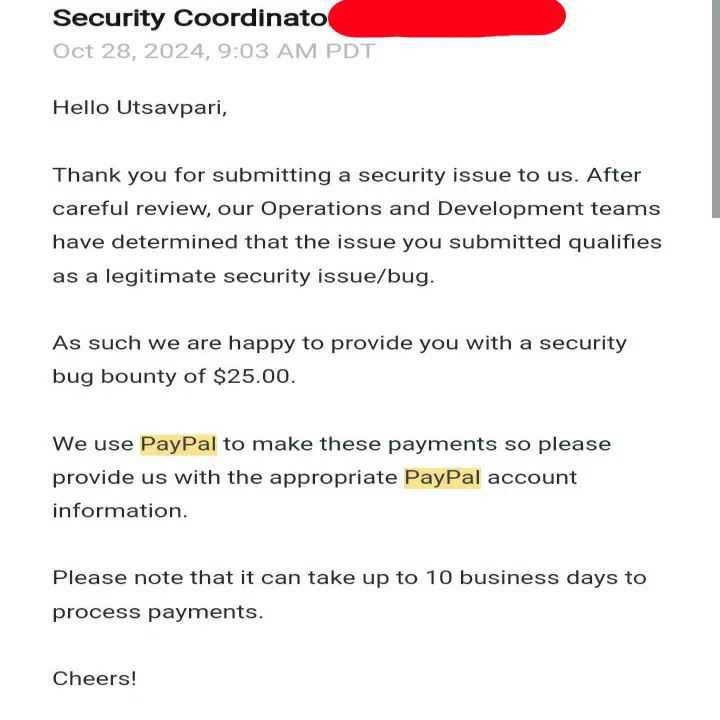
Recently, I revisited one of my previous bug reports, which I had shared in detail earlier.
To my surprise, I found that the vulnerability hadn’t been patched properly and was still reproducible!
I decided to report the issue again to the company, informing them that the initial fix was incomplete. The company acknowledged my findings, implemented a proper fix, and rewarded me with another $25 bounty in addition to the original $25 bounty. That brought the total to $50 for the same bug!
Takeaways for Bug Hunters 🛠️
- Recheck Old Bugs 🔄
Always revisit your previously reported vulnerabilities to see if they’ve been patched properly. Sometimes, companies miss critical aspects during their initial fixes. - Communicate Clearly 📝
If you notice that a bug is still exploitable, provide the company with detailed information and evidence. Many reputable companies value this feedback and will acknowledge your efforts. - Persistence Pays 💡
This experience reminded me that persistence and thoroughness can lead to unexpected rewards.
Thank you for reading this short story! Remember to keep testing, keep reporting, and always strive to make the web a safer place.
Keep Hacking, Stay Secure! 🔐
MR. X FACTOR
🔗 Handles:
- Linktree: https://linktr.ee/mrxfact0r_99