Hello, Hackers! 👋
Hope you're all doing well. Today, I’m excited to share another bug I found, which earned me a $100 bounty. So, let’s dive in! 🚀
The Bug Discovery 🐛
The bug was simple yet effective. I was hunting on the site login.target.com and decided
to use paramspider to find any interesting parameters.
paramspider -d login.target.com
I came across a particularly interesting URL endpoint: /status. When I visited this
endpoint, I saw some server information. However, I noticed a parameter: ?full=FUZZ.
I tried several inputs for the full parameter, but nothing worked at first. Then, a
thought crossed my mind. 🤔 I changed full=false no change. But then I switched it to
full=true, and BOOM! 💥 I was able to access the full server status and additional
information about the running server.
Tip 💡
Add /status and /status?full=true to your wordlist for future tests. It
might come in handy!
Bug Reporting 📝
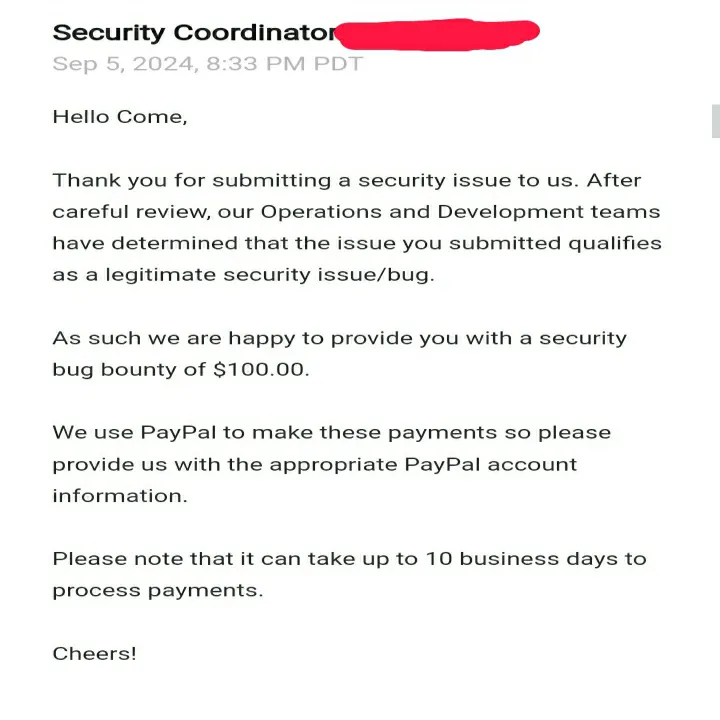
I immediately reported the bug. A few days later, the team validated it, successfully mitigated the issue, and rewarded me with a $100 bounty! 💰
Final Thoughts 💭
That’s the short story of how I found the bug. I hope you learned something useful from it. Remember to keep hunting, keep hacking, and always stay curious! 🔍
Thank you,
MR. X FACTOR
Handles:
- Linktree: https://linktr.ee/mrxfact0r_99