Hello Hackers,
I hope this message finds you well. Firstly, I'd like to apologize for the absence of bug bounty stories since July. Life took a turn as I embarked on my MCA journey, bringing with it the inevitable pressures of academics and college responsibilities. Finding time for bug bounty pursuits and other ethical hacking activities became a challenge. However, I recently completed my first semester exams with an SGPA of 8.57, granting me a brief 10-day break.
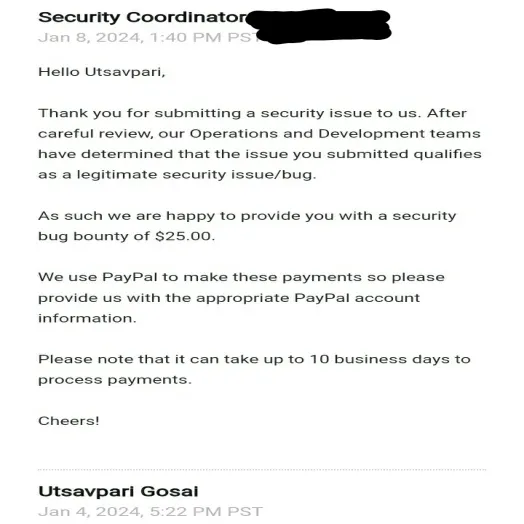
During this mini-vacation, I dedicated time to practice and engage in bug bounty activities. I submitted numerous bug reports during this period, which are currently in the pending and reviewing stage. Reflecting on past reports, I discovered a bug related to text injection that went unnoticed by the company a month ago. Undeterred, I re-reported the issue with additional proof of concept and detailed explanations. This time, the company acknowledged the bug, accepted my findings, and rewarded me with a bounty.
This experience taught me the importance of persistence. If you are confident about a bug but face resistance from the company, it's crucial to reevaluate and communicate effectively. Submitting additional details and proofs can make a significant difference. My main motivation in sharing these stories is to assist beginners and bug bounty hunters at any level. I hope this tale inspires others to persevere and secure both the companies they work with and the bounties they deserve.
Thank you for taking the time to read my story. If you are a beginner or an experienced bug bounty hunter and find this information valuable, feel free to reach out with any questions or suggestions. I am always eager to exchange knowledge and insights.
Wishing you all continuous learning and security in this digital realm.
MR.X
FACTOR
🔗 Handles:
- Linktree: https://linktr.ee/mrxfact0r_99