Hello Hackers,
The story goes like this: I stumbled upon a new program on HackerOne and decided to try my luck. After randomly selecting a program, I initiated my hunt. The target had a registration page, and that’s where the adventure began.
I entered a malformed input in the first name and last name fields, using “http://evil.com" and {{7*7}} as an SSTI check payload. Surprisingly, there were no restrictions. I completed the registration process, proceeded to the dashboard to explore other potential bugs, and that’s when my mind was blown.
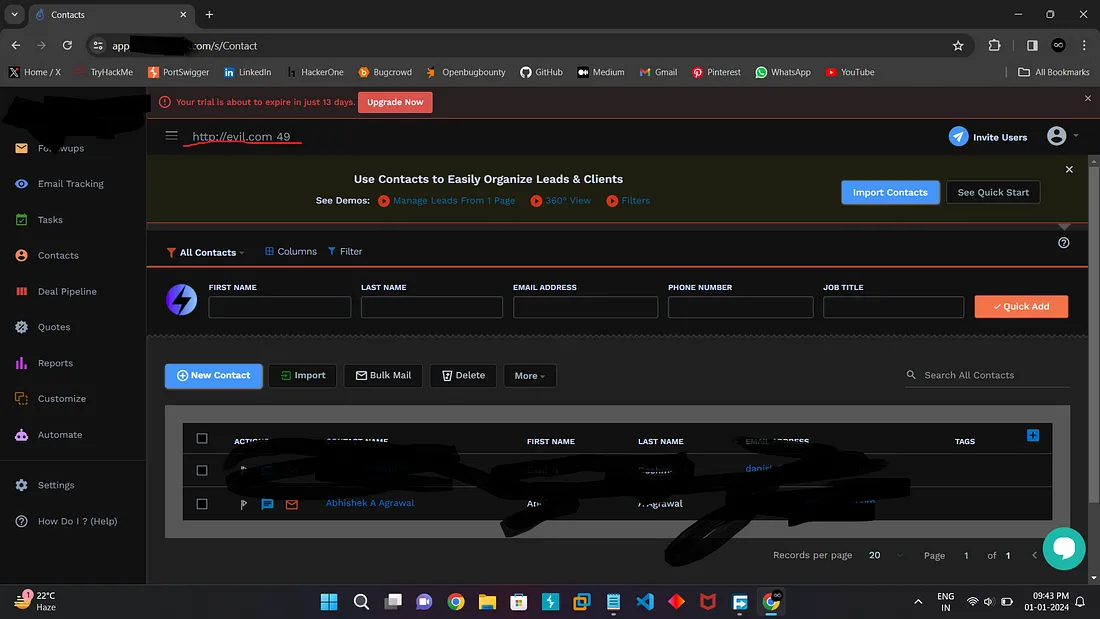
To my amazement, my name appeared at the top as “http://evil.com 49.” I was beyond thrilled. I had unintentionally injected an SSTI payload and achieved unexpected results. Excited about my discovery, I did further research using Google, successfully exploited the vulnerability, and created detailed reports along with PoCs.
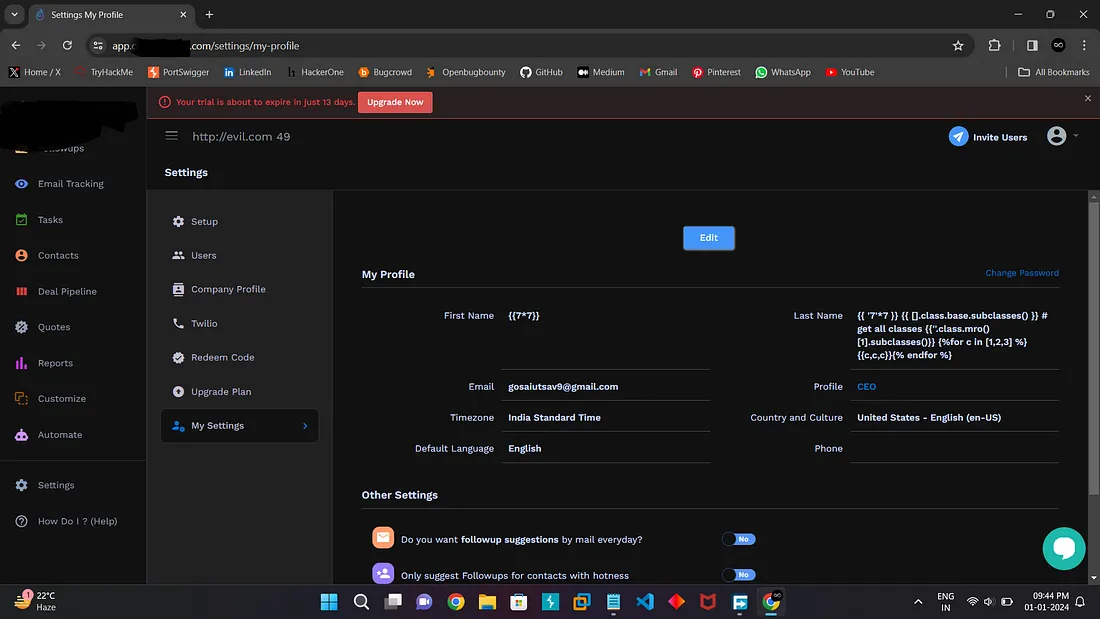
However, my joy was short-lived. Upon attempting to submit my findings on HackerOne, I discovered that the program was no longer accepting submissions and was closed. My heart sank, but undeterred, I reported the critical bug directly to the program’s email address. Despite the setback, I was content with the knowledge gained from learning new functions and the exploitation of SSTI.
Takeaways:
- Always read the program’s guidelines and rules before diving into hunting.
- In moments of disappointment, remind yourself that it’s okay; you’ve acquired new skills and techniques for the future. Trust that these experiences will benefit you in the long run.
I hope you find this article both informative and interesting. If I made any mistakes, please feel free to point them out. I appreciate your feedback.
Thank You,
MR.X FACTOR
🔗 Handles:
- Linktree: https://linktr.ee/mrxfact0r_99