Hello Hackers,
Today, I would like to share my fourth successful bounty, which involved sensitive information disclosure and rewarded me with a $100 bounty. I cannot disclose the company's name due to certain rules and regulations, but I will outline the bug and how I discovered it.
The bug I found was related to a website using WordPress. It all started when I visited the website
and noticed that it was using WordPress, which was revealed by Wappalyzer. Curiosity led me to
investigate further. I right-clicked on an image on the website and opened it in a new tab. The
image URL looked something like this:
https://etc1.etc.com/wp-content/uploads/2022/12/image.png.
Here's where the magic happened. I manipulated the URL, changing it to
/wp-json/wp/v2/users, and to my surprise, it exposed a wealth of sensitive information.
I was able to access usernames, user IDs, descriptions, profile URLs, and other confidential data,
including details about the admin account.
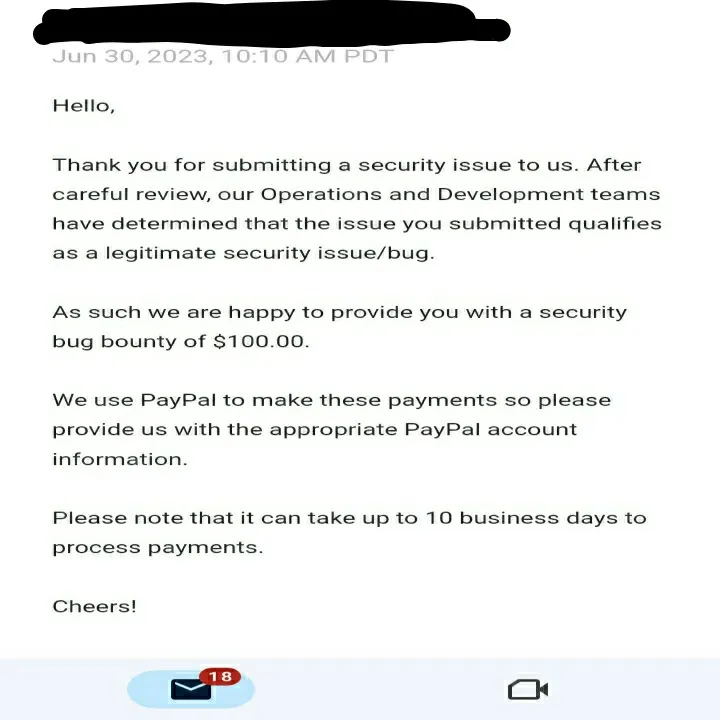
Without hesitation, I reported this vulnerability to the company responsible for the website. After patiently waiting for 15 days, I received a response confirming that my bug report had been accepted, and they rewarded me with a $100 bounty.
I hope this story serves as a valuable learning experience for you, inspiring you to explore and discover similar bugs in your own endeavors. Remember, responsible disclosure is crucial in these situations, and ethical hacking can lead to both personal growth and financial rewards.
Thank You for reading.
Best Regards,
MR.X FACTOR
🔗 Handles:
- Linktree: https://linktr.ee/mrxfact0r_99