#include <stdio.h>#include <pentesting.bughunting>
void Story() {
Printf("
Hello, hackers!
Today, I will share with you a small story about content spoofing or text injection, which earned me a $25 bounty while I was traveling.
So, I was hunting for a program that included a Content Spoofing Vulnerability. Understanding that content spoofing is very effective in social engineering attacks, I decided to try something interesting while I was on the bus heading to my uncle's home.
With some free time on my hands, I opened my mobile's terminal, ran dirsearch, waybackurls, and viewed the source code, among other techniques. Eventually, I came across a parameter called "op=" which I manipulated to "hacked", and it was reflected on the screen. I then attempted to inject XSS and SSTI payloads, but there were filters in place. I reported the issue as required by the company, and they accepted it as a valid bug. As a token of appreciation, they sent me $25 to my PayPal account.
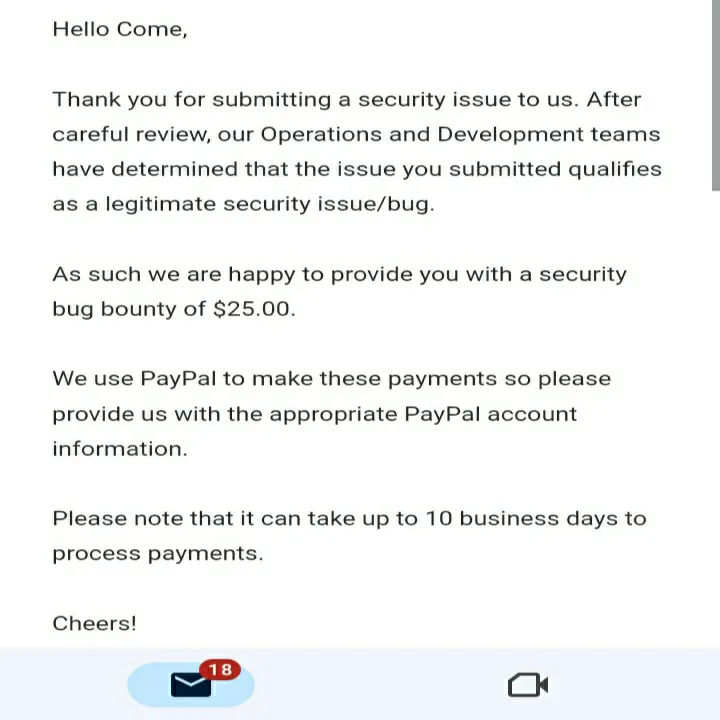
This is a small story of how I earned $25 while traveling. I am grateful to God, my family, and a special person who always supports me.
Thank You,
MR.X FACTOR
");return 1;}Int main(){Story();}
🔗 Handles:
- Linktree: https://linktr.ee/mrxfact0r_99