root@mrxfactor:~#whoami
I am a 20-year-old Ethical Hacker, Application Security and Cyber Security Analyst, and Bug Hunter.
This is my first write-up to share knowledge with beginners or anyone who can benefit from my experience. I am from Gujarat and I started learning about ethical hacking and cyber security 3 years ago. I started bug bounty hunting 5 or 6 months ago during my free time while learning and preparing for my career.
It all started about 5 to 6 months ago when I decided to start bug hunting and aimed to find at least one bug and earn a bounty by the age of 20. I hunted on many sites with bug bounty programs, and even some that did not have them, to help keep companies secure. I found various bugs such as XSS, open redirect, CSRF, etc., but I received my first bounty from a big company, which I will not disclose its name, but it's very big stock and share market company's website let's assume its name is "target.com".
Before sharing my first bounty story, I want to tell any bug bounty beginners that I faced 5 duplicates, 8 not applicable, and 7 informative reports before receiving my first bounty. Additionally, I found this bug on a 15-year-old Intel Premium 4 computer with 2GB RAM, 80GB hard drive, which my uncle and aunt gave me 7 months ago. So, don't fear and become depressed from failures because failures teach you and increase your knowledge. Failures are sent by God to strengthen you, give you more knowledge, so accept them and thank God for them. Now, let's get started.
The bug I found is an information disclosure. I enumerated target.com's subdomains and found one subdomain, let's assume it is "xyz.target.com", that showed a timestamp in milliseconds. I felt weird, so I ran Dirsearch on that domain.
Tip: Always fuzz those domains where you see anything weird or nothing at all.
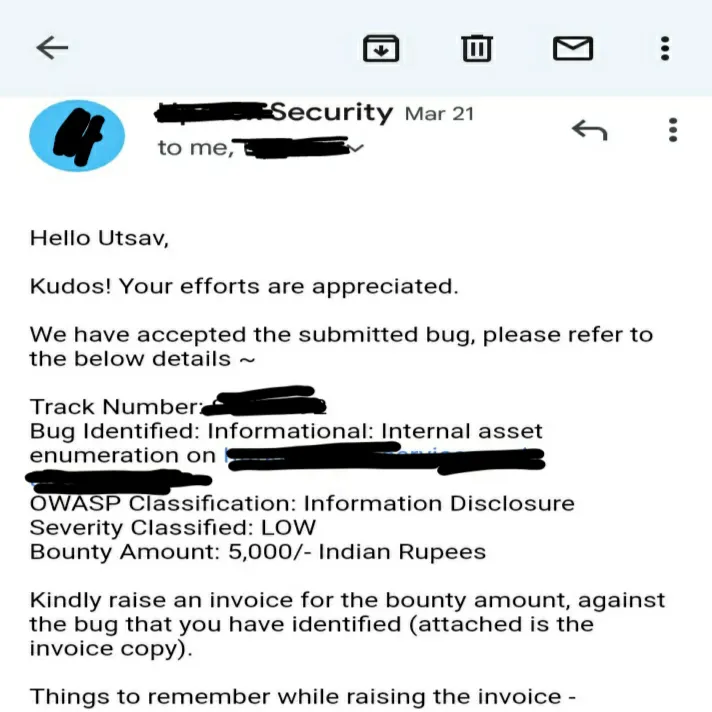
I ran Dirsearch and found an error code 400 in "xyz.target.com/servlet/%C0%AE%C0%AE%C0%AF". Dirsearch is a powerful tool that fuzzes with encodings, and it showed some internal paths, IP addresses, and codes. So, I reported it as an information disclosure, and after four days, the company replied to me, "Your bug has been accepted, and we will reward you a bounty of 5,000 Indian rupees." I was very happy to receive this email and my first bounty. I thanked my God, who gave me strength, blessings, and knowledge from my failures. Therefore, keep going, don’t stop or become depressed, and one day, your God will give you all that you want. Keep your faith in Him, work hard, and
Keep Hunting & Hacking.
I want to thank my God, the biggest hacker Shiva (The Destroyer), my grandfather, grandmother, my mom, dad, my family, and [YSBzcGVjaWFsIHBlcnNvbiB3aG8gaXMgZm9yZXZlciB3aXRoIG1lIGFuZCBhbHNvIGluY2x1ZGVkIGluIG15IGZhbWlseQ==] for always supporting me. I received my first important success in my Ethical Hacking Career.
Thank You,
MR.X FACTOR
🔗 Handles:
- Linktree: https://linktr.ee/mrxfact0r_99